Experienced Leadership. Practical Cybersecurity.
Fractional CISO and cybersecurity advisory from an executive who has owned the problems firsthand.
About NTD Consulting
NTD Consulting provides fractional CISO and cybersecurity advisory services to growing and regulated organizations.
The firm was founded to provide companies with experienced executive security leadership without requiring them to build a large consulting engagement or hire a full-time CISO before they need one.
NTD is also the creator of Mirino Labs, a vendor risk management platform built on that same operating experience.
Ron Moore
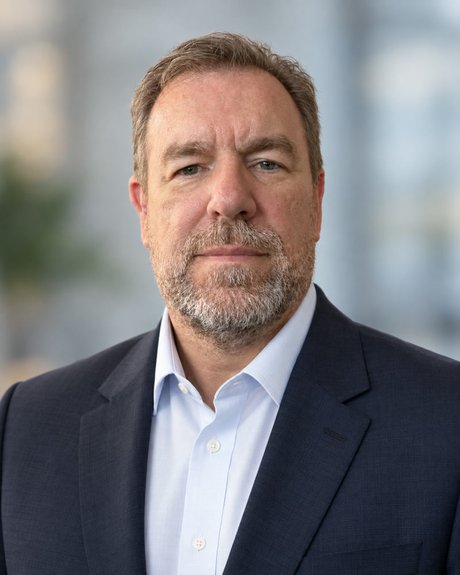
Founder & Principal Consultant
Founder | Fractional CISO | Technology & Cybersecurity Executive
Ron Moore has more than 20 years of experience building, scaling, and protecting technology organizations, with extensive experience in financial services, payments, FinTech, and digital assets.
Most recently, he served as CISO and VP of Technology for a Nasdaq-listed crypto FinTech company. His responsibilities included cybersecurity strategy and operations, security governance, audit and compliance activities, incident response, cloud and technology risk, executive reporting, and supporting the organization through its transition to a public company.
His broader career includes senior technology leadership roles in financial services and payments, building and leading technology teams and operating in organizations ranging from growth-stage businesses to large public companies.
Security has been a major part of his work in recent years, but his perspective extends beyond security controls. He understands the operational, technology, financial, regulatory, and organizational realities that influence whether a security program succeeds.
The NTD Approach
Understand the business first
Security priorities should reflect how the company operates, what it protects, how it makes money, and where meaningful risks exist.
Prioritize what matters
Not every finding deserves the same urgency, investment, or executive attention.
Make risk understandable
Executives and boards need cybersecurity translated into business decisions rather than technical terminology.
Build sustainable programs
Controls should work in the real organization, not just on paper.
Stay independent
The objective is to provide leadership and judgment — not to create unnecessary projects or sell security products.
Schedule a Conversation
Start with a conversation about the business, the security program, and what matters most.